A portable binary format can provide useful isolation, but the surrounding host, imported functions, and resource limits define the application’s actual exposure.
A larger pixel count can support detail and cropping, but optics, focus, motion, processing, and delivery determine whether that capacity becomes visible value.
Understanding the difference between running workloads and the control system that schedules, updates, and reconciles them helps teams prepare realistic recovery plans.
Browser privacy boundaries can change how embedded services recognize users. Here is how to reason about login, storage, and graceful fallback without weakening privacy.
Caching decisions become clearer when teams distinguish reusable assets, changing public information, and personalized responses before selecting directives.
Model weights are only part of inference memory. Context length, active requests, cache strategy, and generation limits shape the capacity a service can actually provide.
One-way event streams can simplify live updates, but event identity, reconnection, cancellation, and visible state determine whether the interface stays trustworthy.
Software bills of materials can improve component visibility, but accurate release mapping, ownership, and a response process turn the inventory into useful operations.
Service workers can support offline experiences, but data ownership, queued writes, conflict resolution, and update behavior determine whether the feature is dependable.
Separating compilation from execution can make an image smaller and easier to maintain, provided the final stage retains the dependencies, diagnostics, and update path the application needs.
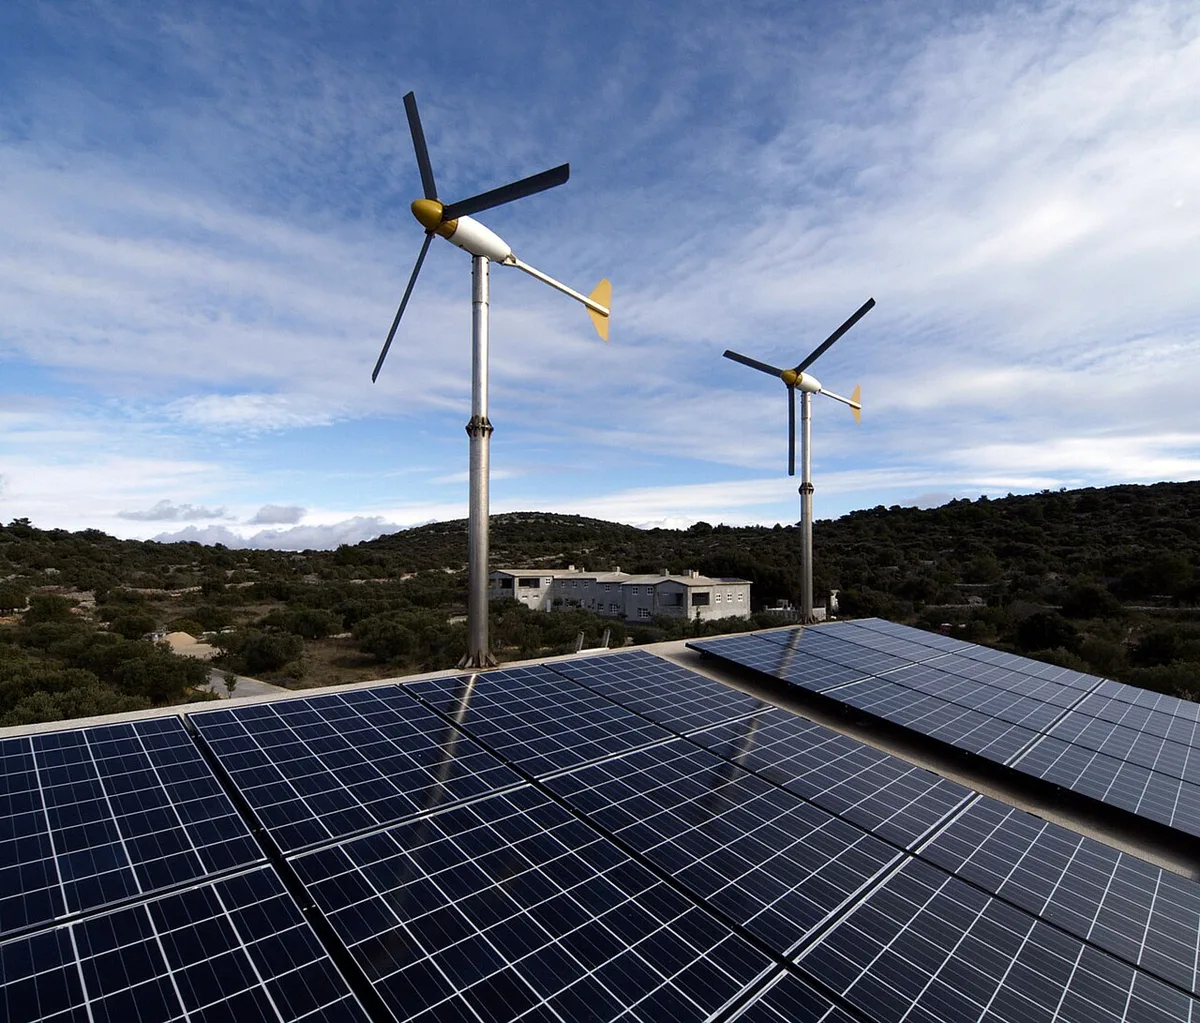
The September 2026 US Wind Turbine Database release is a useful guide to reading infrastructure data, technical specifications and the limits of a point on a map.
Tags make releases convenient to discuss, while digests identify content. Reliable deployment records need both human meaning and exact artifact identity.
Modern OAuth guidance helps protect authorization flows. Application teams still need precise redirect handling, token scope, session design, and a clear sign-out story.
Requests influence placement and limits influence runtime behavior. Useful settings come from representative measurements, startup patterns, and the consequences of contention.
Base backups and archived WAL can support recovery to an earlier state, but retention, missing segments, credentials, and application validation decide whether the plan works under pressure.
A pool controls access to database work, not the amount of work the database can complete. Size it around measured demand, transaction behavior, and a clear waiting policy.
A nonce- or hash-based CSP can narrow script execution, but caching, third-party loaders, reporting, and application integration decide whether the policy remains effective.
A staged schema change can preserve compatibility across rolling deployments, but backfills, old clients, constraints, and rollback need to be designed together.
Asynchronous replicas can distribute read work, but read-after-write expectations, authorization changes, lag signals, and failover need a deliberate consistency policy.
Local reuse can reduce network work, but cache coherence depends on tracking, reconnection behavior, bounded storage, and an explicit policy for stale application data.
Reliable messaging needs coordinated publisher confirms, consumer acknowledgements, duplicate handling, and a clear definition of when responsibility has transferred.
RFC 9849 defines ECH, while deployment depends on configuration discovery, client and server support, network conditions, and careful interpretation of privacy diagnostics.
Idempotency can make uncertain writes safer to retry, but key scope, request consistency, retention, and reconciliation determine what the application can actually guarantee.
Distributed tracing helps explain a request only when context survives boundaries, spans describe meaningful work, and sampling limitations remain visible to investigators.
Error-budget alerts can connect monitoring to user impact, but the indicator, traffic assumptions, response window, and runbook must form a coherent operating policy.
Optional and runtime permissions can make extension authority more understandable, while denial handling, update review, local-file access, and data flow determine the real boundary.
Flags can separate release from rollout, but evaluation context, safe defaults, cross-service consistency, and cleanup determine whether they remain useful controls.
A lockfile records dependency resolution, but package-manager versions, install settings, platform differences, scripts, and maintenance policy still shape the build.
Browser GPU access can support demanding computation and graphics, but limits, device loss, resource budgets, and an honest fallback determine the usable product.
Browser media processing requires coordinated codec support, timestamps, frame ownership, queue control, and container handling to produce a reliable result.
Modern image formats can reduce transfer, but visual quality, encoding cost, decoding, dimensions, caching, and fallback determine the result readers actually experience.
Resolution selection and art direction solve different problems. Accurate layout hints, useful crops, stable dimensions, and deployed-page checks make responsive photography work.
A modal is an interaction state, not just a centered panel. Focus entry, keyboard behavior, labeling, background treatment, and return paths determine whether it is usable.
Respecting motion preferences requires more than shortening every transition. The interface still needs clear state, progress, spatial relationships, and usable controls.
COOP and COEP can establish a special browser isolation state, but resource permissions, popup relationships, deployment consistency, and required features need a coordinated plan.
A privacy-respecting app connects permissions to a visible task, uses narrower platform alternatives where suitable, and remains useful when access is limited or withdrawn.